Threat Advisory: The Dangers of Long Dwell Malware
Long dwell malware like BRICKSTORM and Daxin can sit undetected for years. UltraViolet TIDE breaks down the tradecraft and how to respond.
Benchmarks your AI security practices against peer data.
Find flaws in AI Systems
Find flaws in web, mobile, and IoT applications.
Live-fire exercises to sharpen detection and response.
Time-boxed security assessments across networks, apps, and infrastructure.
Simulated attacks to test detection and incident response.
Named security experts integrated seamlessly into your team.
Real-time detection and automated threat response.
24x7 monitoring and response by expert analysts.
Detection-focused SIEM migration without visibility gaps.
UltraViolet's proprietary AI platform powering all application penetration testing.
Unified security platform powering all UV services.
Automated detection engineering across your security platforms.
Cross-platform toolkit for advanced red team ops.
UltraViolet Cyber provides security services across the AI lifecycle, combining strategy, threat modeling, adversarial testing, monitoring, and training to support secure AI adoption.
How a global financial software company keeps hundreds of marketplace applications moving through a ...
Secure your code, infrastructure, and deployment pipelines before attackers exploit them.
Before you trust a MITRE ATT&CK coverage number, run it through three questions. Here's what to ask, and why each one ...
UltraViolet's AISec Study uses an interview-based methodology to score AI security maturity across 10 organizations. Read ...
UltraViolet Cyber is a practitioner-led MSSP delivering offensive and defensive security to Global 2000 and Federal clients. Built by former intelligence operators, we unify application security, red teaming, detection, and engineering under one roof. Our UV Lens platform replaces silos with integrated, outcome-driven operations.
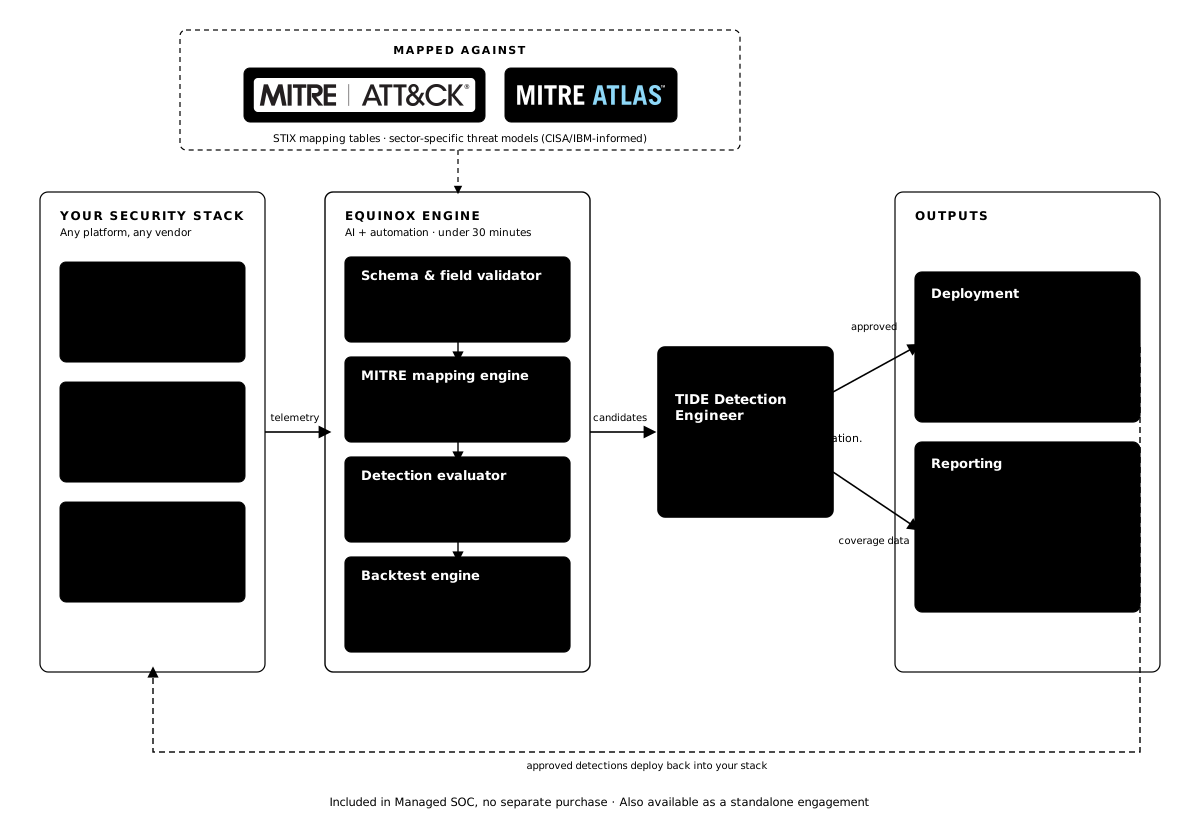
Equinox is UltraViolet Cyber’s detection engineering platform, built and operated by our TIDE team. In under 30 minutes, it assesses detections and telemetry accross your EDR and SIEM platforms, mapping them to MITRE ATT&CK and MITRE ATLAS, showing where coverage exists and where gaps remain.
Enabling every vendor detection buries analysts in alerts.
Manual coverage mapping takes weeks of analysis.
Frameworks, telemetry, and threats change constantly.
Equinox surfaces coverage gaps in minutes: automation maps coverage against MITRE, and TIDE engineers decide what deploys.
For Security Executives
For SOC & Detection Engineering Leads
01. LOG SOURCE & SCHEMA INVENTORY
Equinox inventories detection and integrated log source and inspects available fields and schemas. You see which detections your data can support.
02. MITRE COVERAGE MAPPING
It maps your detections and telemetry to MITRE ATT&CK and MITRE ATLAS to show mapped coverage, gaps, and priorities. Analysis completes in under 30 minutes.
03. VENDOR-FIRST RECOMMENDATIONS
Equinox evaluates your existing vendor detections first, then recommends custom detections where none fit. TIDE engineers review recommendations and develop custom detections as needed.
04. BACKTESTED DEPLOYMENT
TIDE engineers backtest recommended detections against 30 days of historical data. Those exceeding 30 alerts require further review. Only approved detections deploy.
Equinox validates schemas, maps coverage, and evaluates candidate detections in under 30 minutes. Approved candidates are backtested before deployment into your stack.
Most environments already collect the telemetry to support far more coverage than they have enabled. In one customer assessment, Equinox validated a path from 26.6% to 61.3% mapped MITRE ATT&CK technique coverage, a potential 130% relative increase, with no expected increase in SOC alert volume.
Equinox assesses coverage and recommends improvements for TIDE review. Quarterly Managed SOC assessments track coverage as threats, frameworks, and telemetry change.
Every Detection Earns Its Place and Is Built for Your Environment
Equinox findings guide inform purple team exercises and give UltraViolet's SOC analysts a clearer coverage map. When Offensive Security engagements expose detection gaps, Equinox helps TIDE prioritize improvements. Offense informs defense. Defense sharpens offense. Combined findings inform a more complete remediation roadmap.
Learn more about Equinox.
TIDE, UltraViolet’s Threat Intelligence & Detection Engineering team, built and operates Equinox. Beyond that work, the team tracks emerging threats, hunts across the environments we protect, and turns those findings into new detection logic.
With Equinox, TIDE engineers review, backtest, tune, and approve recommended detections before deployment. They also use Equinox findings to inform quarterly coverage reviews, purple team exercises, and responses to emerging threats.
Both. Equinox is included with Managed SOC at no additional change, with assessments at onboarding and quarterly thereafter. It is also available as a standalone engagement for organizations operating their own SOC or using another MDR provider.
Emerging threat research from TIDE, UltraViolet's Threat Intelligence and Detection Engineering team. The same intelligence that drives Equinox detections.
Book a 30-minute working session with a TIDE engineer to discuss your detection coverage and how Equinox can help identify gaps.