Threat Advisory: Gunra Ransomware Group Targeting Vulnerable Fortinet Devices
Gunra ransomware exploits two unpatched Fortinet FortiOS/FortiProxy bypass flaws to hit critical infrastructure. Patch and check your MFA now.
Benchmarks your AI security practices against peer data.
Find flaws in AI Systems
Find flaws in web, mobile, and IoT applications.
Live-fire exercises to sharpen detection and response.
Time-boxed security assessments across networks, apps, and infrastructure.
Simulated attacks to test detection and incident response.
Named security experts integrated seamlessly into your team.
Real-time detection and automated threat response.
24x7 monitoring and response by expert analysts.
Detection-focused SIEM migration without visibility gaps.
UltraViolet's proprietary AI platform powering all application penetration testing.
Unified security platform powering all UV services.
Automated detection engineering across your security platforms.
Cross-platform toolkit for advanced red team ops.
UltraViolet Cyber provides security services across the AI lifecycle, combining strategy, threat modeling, adversarial testing, monitoring, and training to support secure AI adoption.
A global professional services and audit company needed evidence of how its AI assistant would hold up under ...
Secure your code, infrastructure, and deployment pipelines before attackers exploit them.
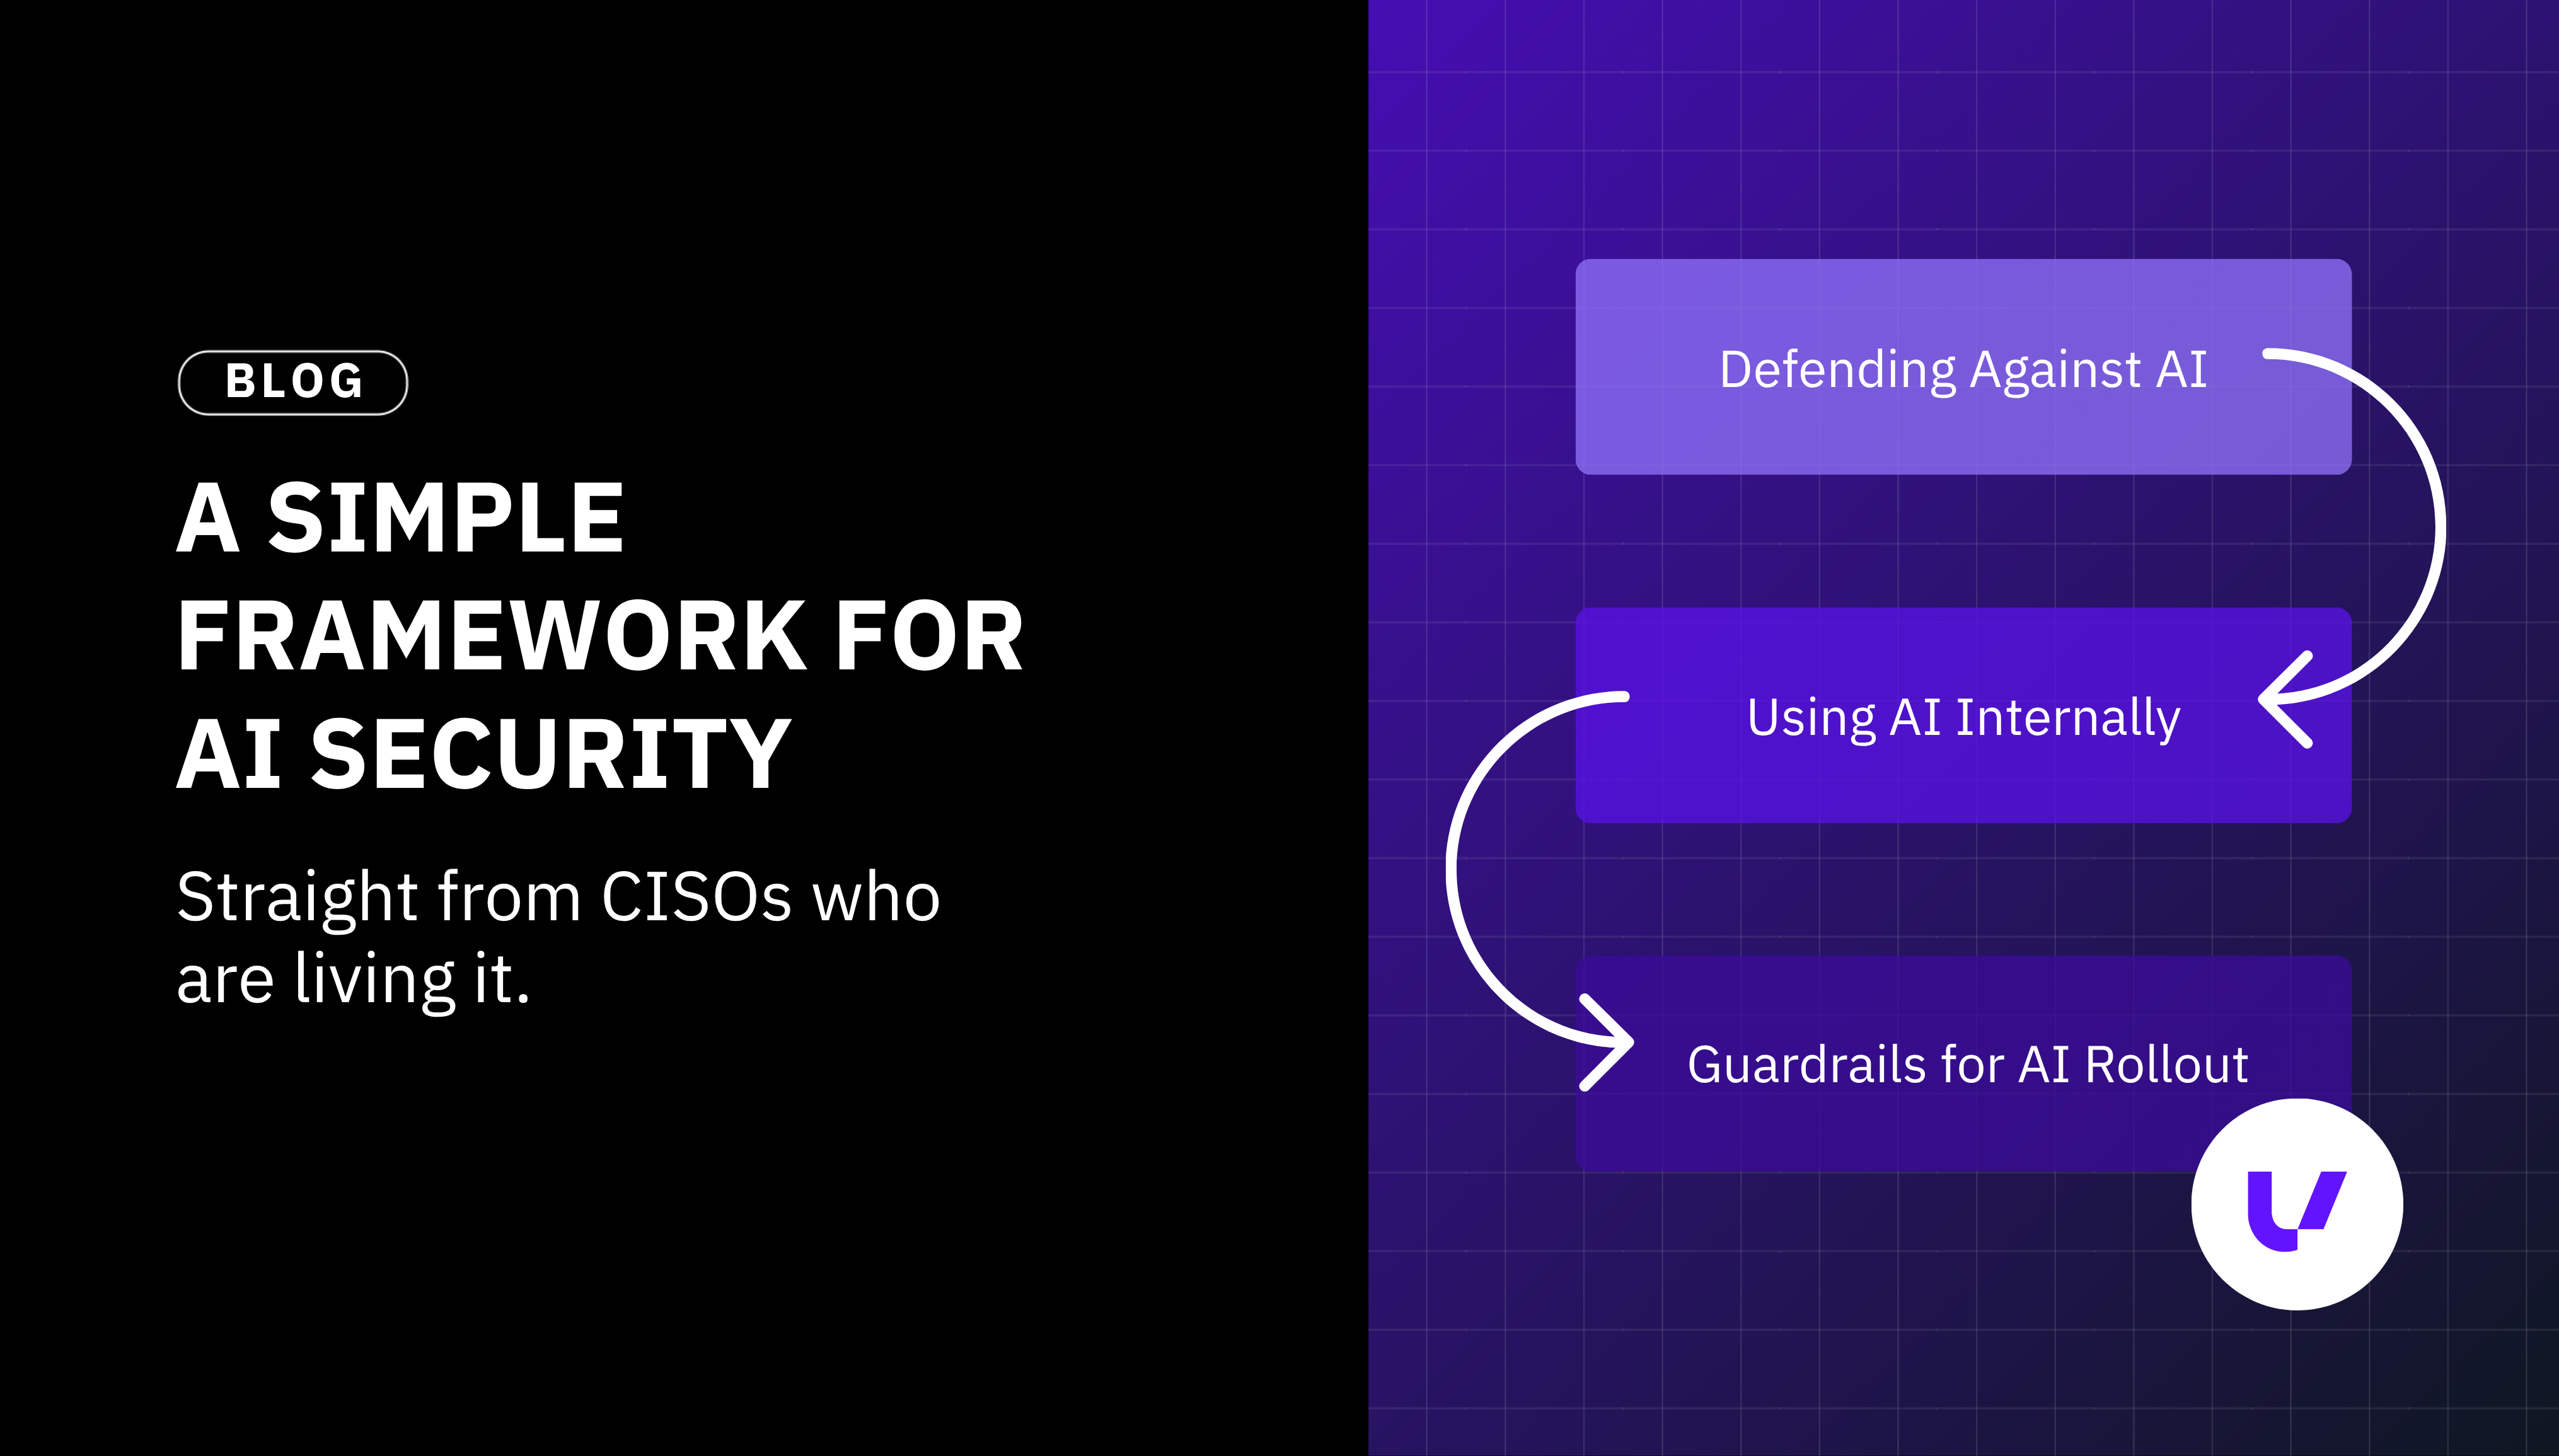
A three-part framework CISOs use to think about AI risk, backed by data on where most security programs are strong, and ...
UltraViolet's AISec Study uses an interview-based methodology to score AI security maturity across 10 organizations. Read ...
UltraViolet Cyber is a practitioner-led MSSP delivering offensive and defensive security to Global 2000 and Federal clients. Built by former intelligence operators, we unify application security, red teaming, detection, and engineering under one roof. Our UV Lens platform replaces silos with integrated, outcome-driven operations.

MCLEAN, Va. — August 27, 2026 — UltraViolet Cyber (UltraViolet), the only security operations partner that unifies red, blue and purple team capabilities into one integrated offering, today announced the launch of Equinox, its proprietary detection engineering platform, built and operated by the Threat Intelligence & Detection Engineering (TIDE) team. Equinox maximizes detection coverage across customers’ Security Information and Event Management (SIEM) and Endpoint Detection and Response (EDR) tooling using AI and automation.
Security environments, telemetry and threat frameworks change constantly. Vendor detection libraries can include thousands of options, but what is relevant depends on each organization's data, technology and risk profile, which can take weeks to manually analyze. Equinox closes that gap: it identifies each customer's current detections and available log sources and maps them against both MITRE ATT&CK and MITRE ATLAS frameworks. UltraViolet is the first to provide a full map and scorecard of coverage status using MITRE ATLAS, specifically for adversarial tactics and techniques targeting AI and machine learning systems. The coverage prescriptively determines where mapped coverage exists, where gaps remain, and which detections or log sources could improve it.
Equinox uses automation to perform the analysis in under 30 minutes, then recommends vendor or custom detections to be built and enabled to fill the identified gaps. UltraViolet’s TIDE engineers then review, backtest, and approve every recommended detection before deployment, tuning it as needed. Customers receive framework-aligned evidence of where mapped detection coverage exists, how mapped coverage is changing and what to prioritize next to maximize coverage without increasing alert volume.
"Every SOC team has heard the question 'are we actually covered?' and struggles to answer it with full confidence," said Dan Gittis, Director, TIDE Team at UltraViolet Cyber. “Equinox gives our TIDE engineers a real answer, in minutes instead of weeks, on not just which detections exist, but validates that a detection can actually fire against the data rather than assuming a mapped rule is effective. That's the difference between a coverage dashboard and coverage you can defend in an audit."
Independent industry research puts average enterprise detection coverage at 21% of MITRE ATT&CK techniques1, suggesting many organizations have telemetry capable of supporting far more mapped coverage than they currently have enabled. In a customer environment, a single Equinox review identified and validated a path from 59 of 222 covered techniques (26.6%) to 136 of 222 (61.3%) after implementation of the recommended detections. This represents a 34.7 percentage-point gain and a 130% increase in mapped technique coverage, achieved without an increase in SOC alert volume.
"Security leaders don't lack detections, they lack visibility into whether the ones they have actually work against their own data,” said Atif Ghauri, Chief Operating Officer of UltraViolet Cyber. “Equinox closes that gap using the telemetry customers already have, before they spend a dollar on anything new. It's a clear example of what we mean by practitioner-led, AI-accelerated: automation does the heavy lifting, our TIDE engineers make the calls that matter."
About Equinox
Equinox is delivered as part of UltraViolet's Managed SOC offering at no additional charge, used during onboarding for every new customer and quarterly thereafter, and is also available as a standalone engagement for organizations that run their own SOC, or for clients that utilize UltraViolet’s embedded security experts. It is vendor-agnostic by design, supporting multiple SIEM and EDR platforms. To learn more about Equinox, visit: https://www.uvcyber.com/solutions/equinox.
About UltraViolet Cyber
UltraViolet Cyber is the only security operations partner that unifies red, blue, and purple team capabilities into one integrated team — finding what's vulnerable, stopping active threats, and validating that your defenses hold under real pressure. Built by former U.S. intelligence community operators with 30+ years of experience, we serve 400+ Global 2000 enterprises and federal agencies. Our practitioner-led and AI-accelerated closed-loop operations turn offensive findings into defensive weapons immediately so gaps close in real time and defenses improve before attackers can exploit what testing uncovers. Offense informs defense. Defense sharpens offense. Security that gets smarter and stronger with every iteration.
UltraViolet is at the forefront of AI security. Purpose-built to test, validate, and govern the AI systems organizations are deploying today, UltraViolet brings the same offensive and defensive rigor to AI that it applies across the enterprise. UltraViolet is ranked #19 on the Top 250 MSSP List and is headquartered in McLean, Virginia. For more information, visit our website, read our blog, or follow us on LinkedIn.
Media Contact
W2 Communications for UltraViolet Cyber ultraviolet@w2comm.com
We’re here to help. Get in touch for an initial conversation with one of our security experts and learn more about how UltraViolet Cyber can help you take cyber readiness and resilience to new levels.