 UltraViolet Solstice
 UltraViolet Lens Platform
 UltraViolet Equinox
 UltraViolet Cyber Acquires Black Duck’s Application Security Testing Services Business
 UltraViolet Cyber Launches Solstice
Blog
A Simple Framework for AI Security, Straight From CISOs Who Are Living It
Before any AI policy gets written, the data underneath it needs an honest look: how clean it is, and who or what already has access to it.
That point came up directly in a string of CISO conversations this year. One security leader made it plainly: an organization with years of accumulated data carries messy, ungoverned data by default. The starting point for AI governance is protecting that existing data from being consumed by AI systems, and settling which identities and services should have access to it in the first place.
Most security organizations already have the AI governance basics in place. Policies exist. Executive sponsors have signed off. Steering committees meet. But the actual data governance needed to support AI is lagging far behind.
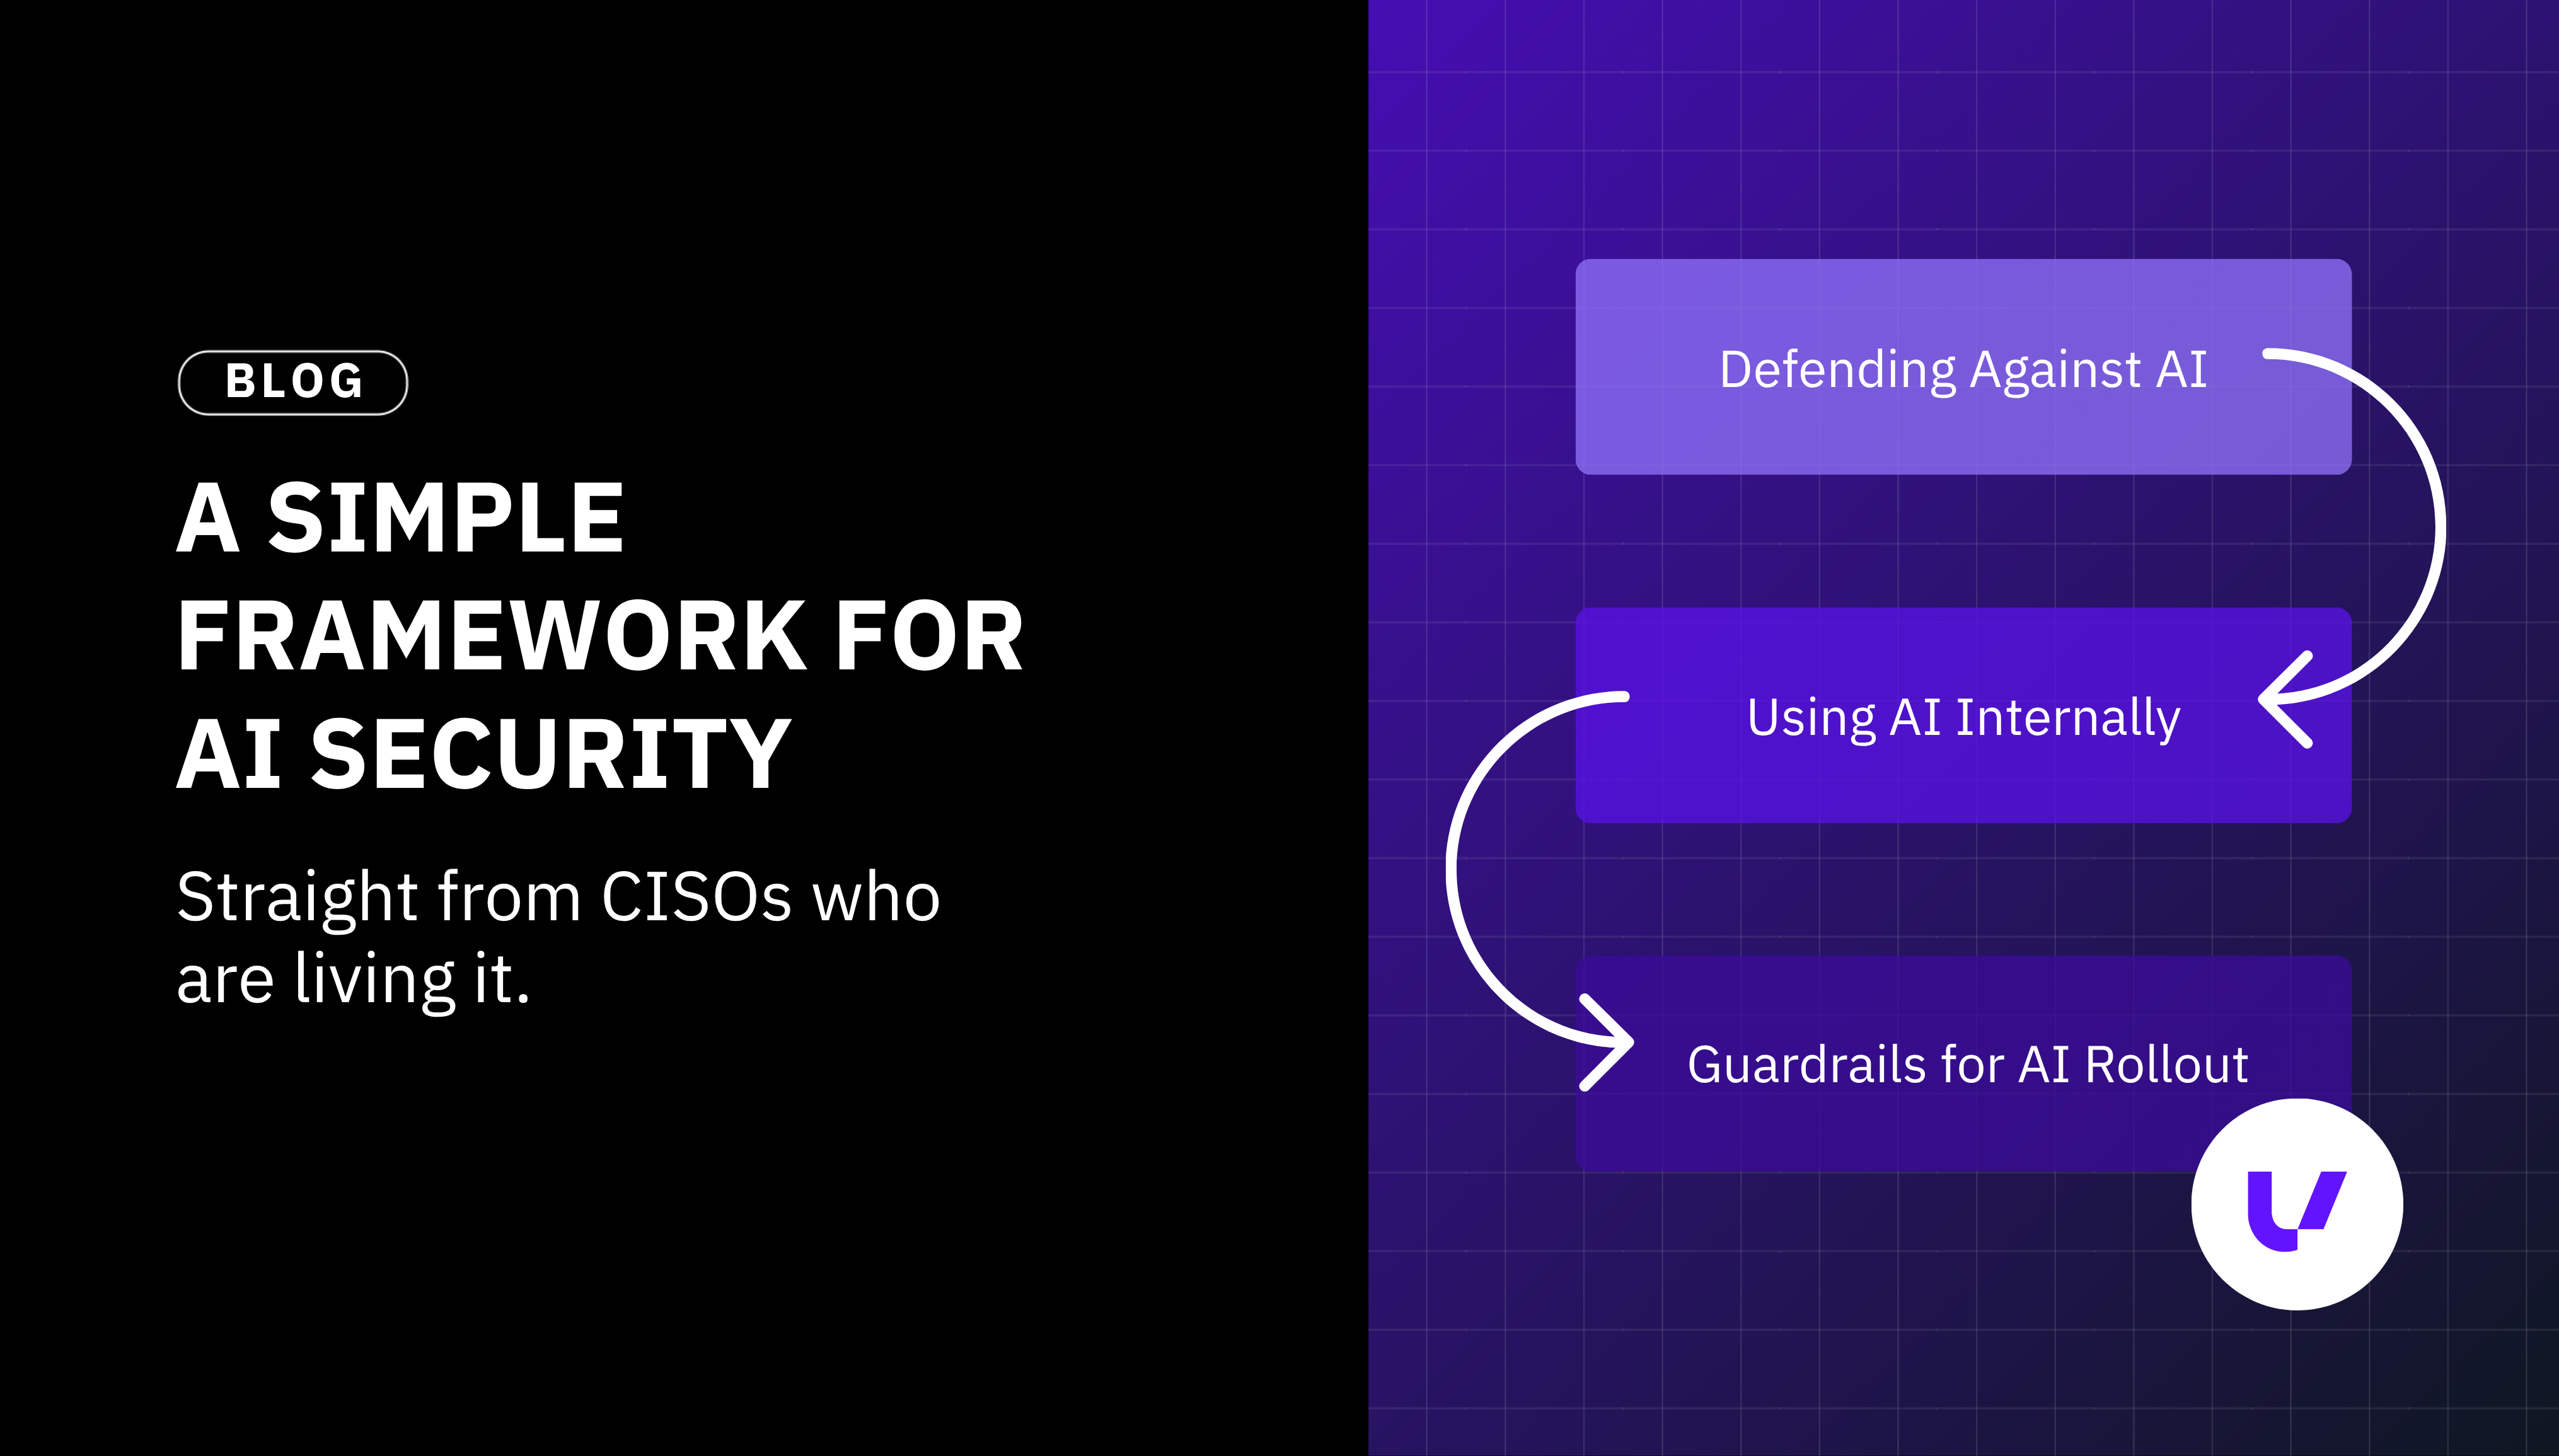
That gap is where a second pattern shows up: a three-part way of describing AI risk that keeps surfacing, almost word for word, in conversations with security leaders across industries.
AI risk in three parts
Ask a CISO how they think about AI risk, and the answer usually splits into three buckets.
Defending against AI. Attackers are using AI to write more convincing phishing content, build malware faster, and find exploitable vulnerabilities in less time than most security teams are used to defending against.
Using AI internally. Security teams are deploying AI and agents inside their own operations to triage alerts faster, summarize investigations, and cut into the manual work that fills a SOC analyst's day. It's the only way understaffed teams can scale to meet their growing workloads.
Guardrails for AI rollout. The rest of the business is shipping AI into customer-facing products and internal workflows right now, usually faster than security can build the testing and monitoring to keep pace. Every new AI feature is a new attack surface the organization built for itself.
Every security program touches all three. Almost none of them are strong in all three at once.
What the data says about that gap
UltraViolet Cyber's AISec Study scored ten organizations, spanning banking, SaaS, healthcare, manufacturing, government, and the nonprofit sector, against 64 discrete AI security activities. Each activity is rated Established (a consistently performed practice, backed by process and tooling), Emerging (partial, piloted, or planned), or Unobserved (no evidence found). Coverage ranged from 43% to 85%, with a median of 55%.
The three buckets above show up directly in the scores. For defending against AI, detection of automated attacks against AI systems was observed, meaning rated Established or Emerging, at just 1 of the 10 organizations, and fully established at none. For using AI internally, AI-augmented security operations ranged from 10% to 90% coverage, the widest spread of any capability in the study. For guardrails for AI rollout, agentic workflow assurance testing, checking that an AI agent does what it's supposed to and nothing else, was observed at 4 organizations and fully established at zero.
Governance is the one part that's ahead of the other two. Boards can see it. Almost none of them can see whether the rest of the framework is actually built.
A quick self-check
Three questions, one for each part, worth asking before the next board update:
- Defending against AI: if an attacker used AI to move faster through reconnaissance or exploit discovery against your environment tomorrow, would your monitoring catch how much faster the attack moved, or only the breach at the end?
- Using AI internally: is AI reducing your team's triage and investigation time today, with numbers to show it, or is it a pilot that hasn't moved past a demo?
- Guardrails for AI rollout: for every AI feature currently in production, can you name who adversarially tested it, and when?
Most programs can answer one of these with confidence. Fewer can answer all three.
Starting AI governance with the data
The data problem underneath all of this doesn't go away because a policy got written. An AI system connected to years of accumulated, ungoverned data inherits every access control gap and every stale permission that data already had. Governance work that starts with the AI tool and skips the data underneath it starts one step too late.
Benchmarking where you stand
UltraViolet Cyber's AISec Program Assessment runs the same 64-activity framework behind the AISec Study against your own organization. It's a confidential, interview-based engagement: security, AI, governance, and engineering leaders walk through how AI is built and governed inside the organization, day to day.
Each activity gets scored Established, Emerging, or Observed, and rolls up into the same 10 capabilities and three domains covered above: direction and oversight, engineering and usage, and assurance and protection. Your coverage score gets placed against a growing pool of peer organizations across banking, healthcare, government, and software, so the results are a benchmark, not just a checklist. You leave with recommendations ranked by which gaps close the most exposure first.
If you can answer all three questions above with confidence, the assessment will confirm it with peer data behind you. If you can't, it'll show you exactly where to start.
ADDITIONAL INSIGHTS
READY TO GET STARTED?
We’re here to help. Get in touch for an initial conversation with one of our security experts and learn more about how UltraViolet Cyber can help you take cyber readiness and resilience to new levels.