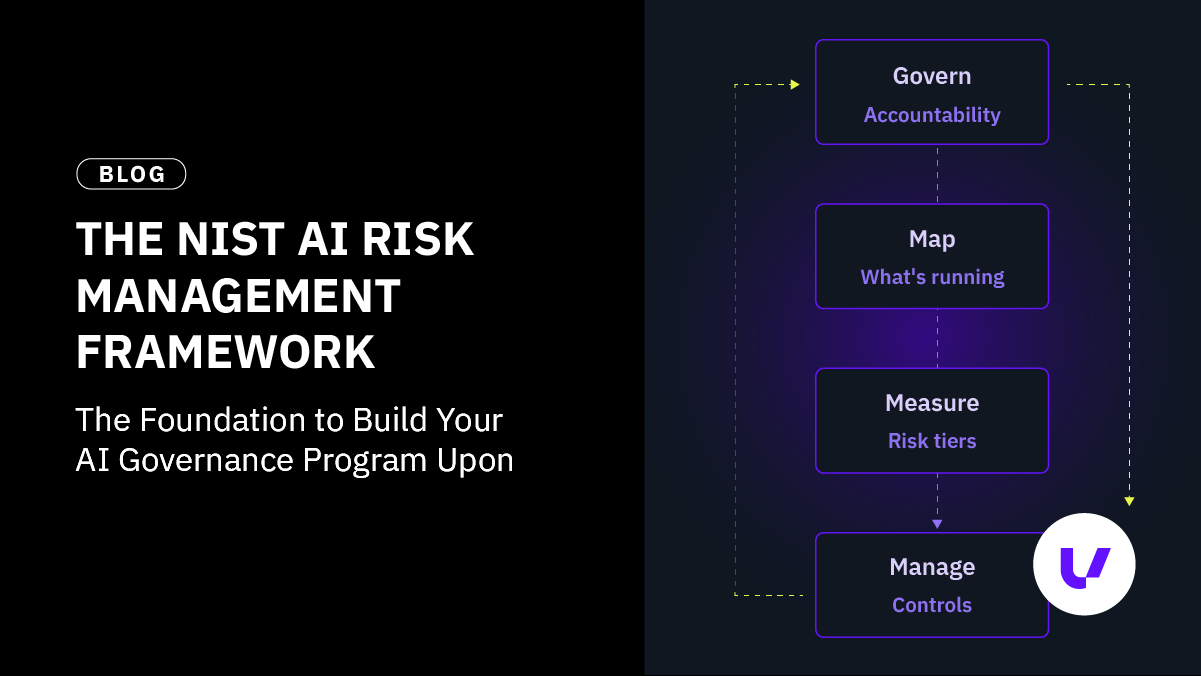
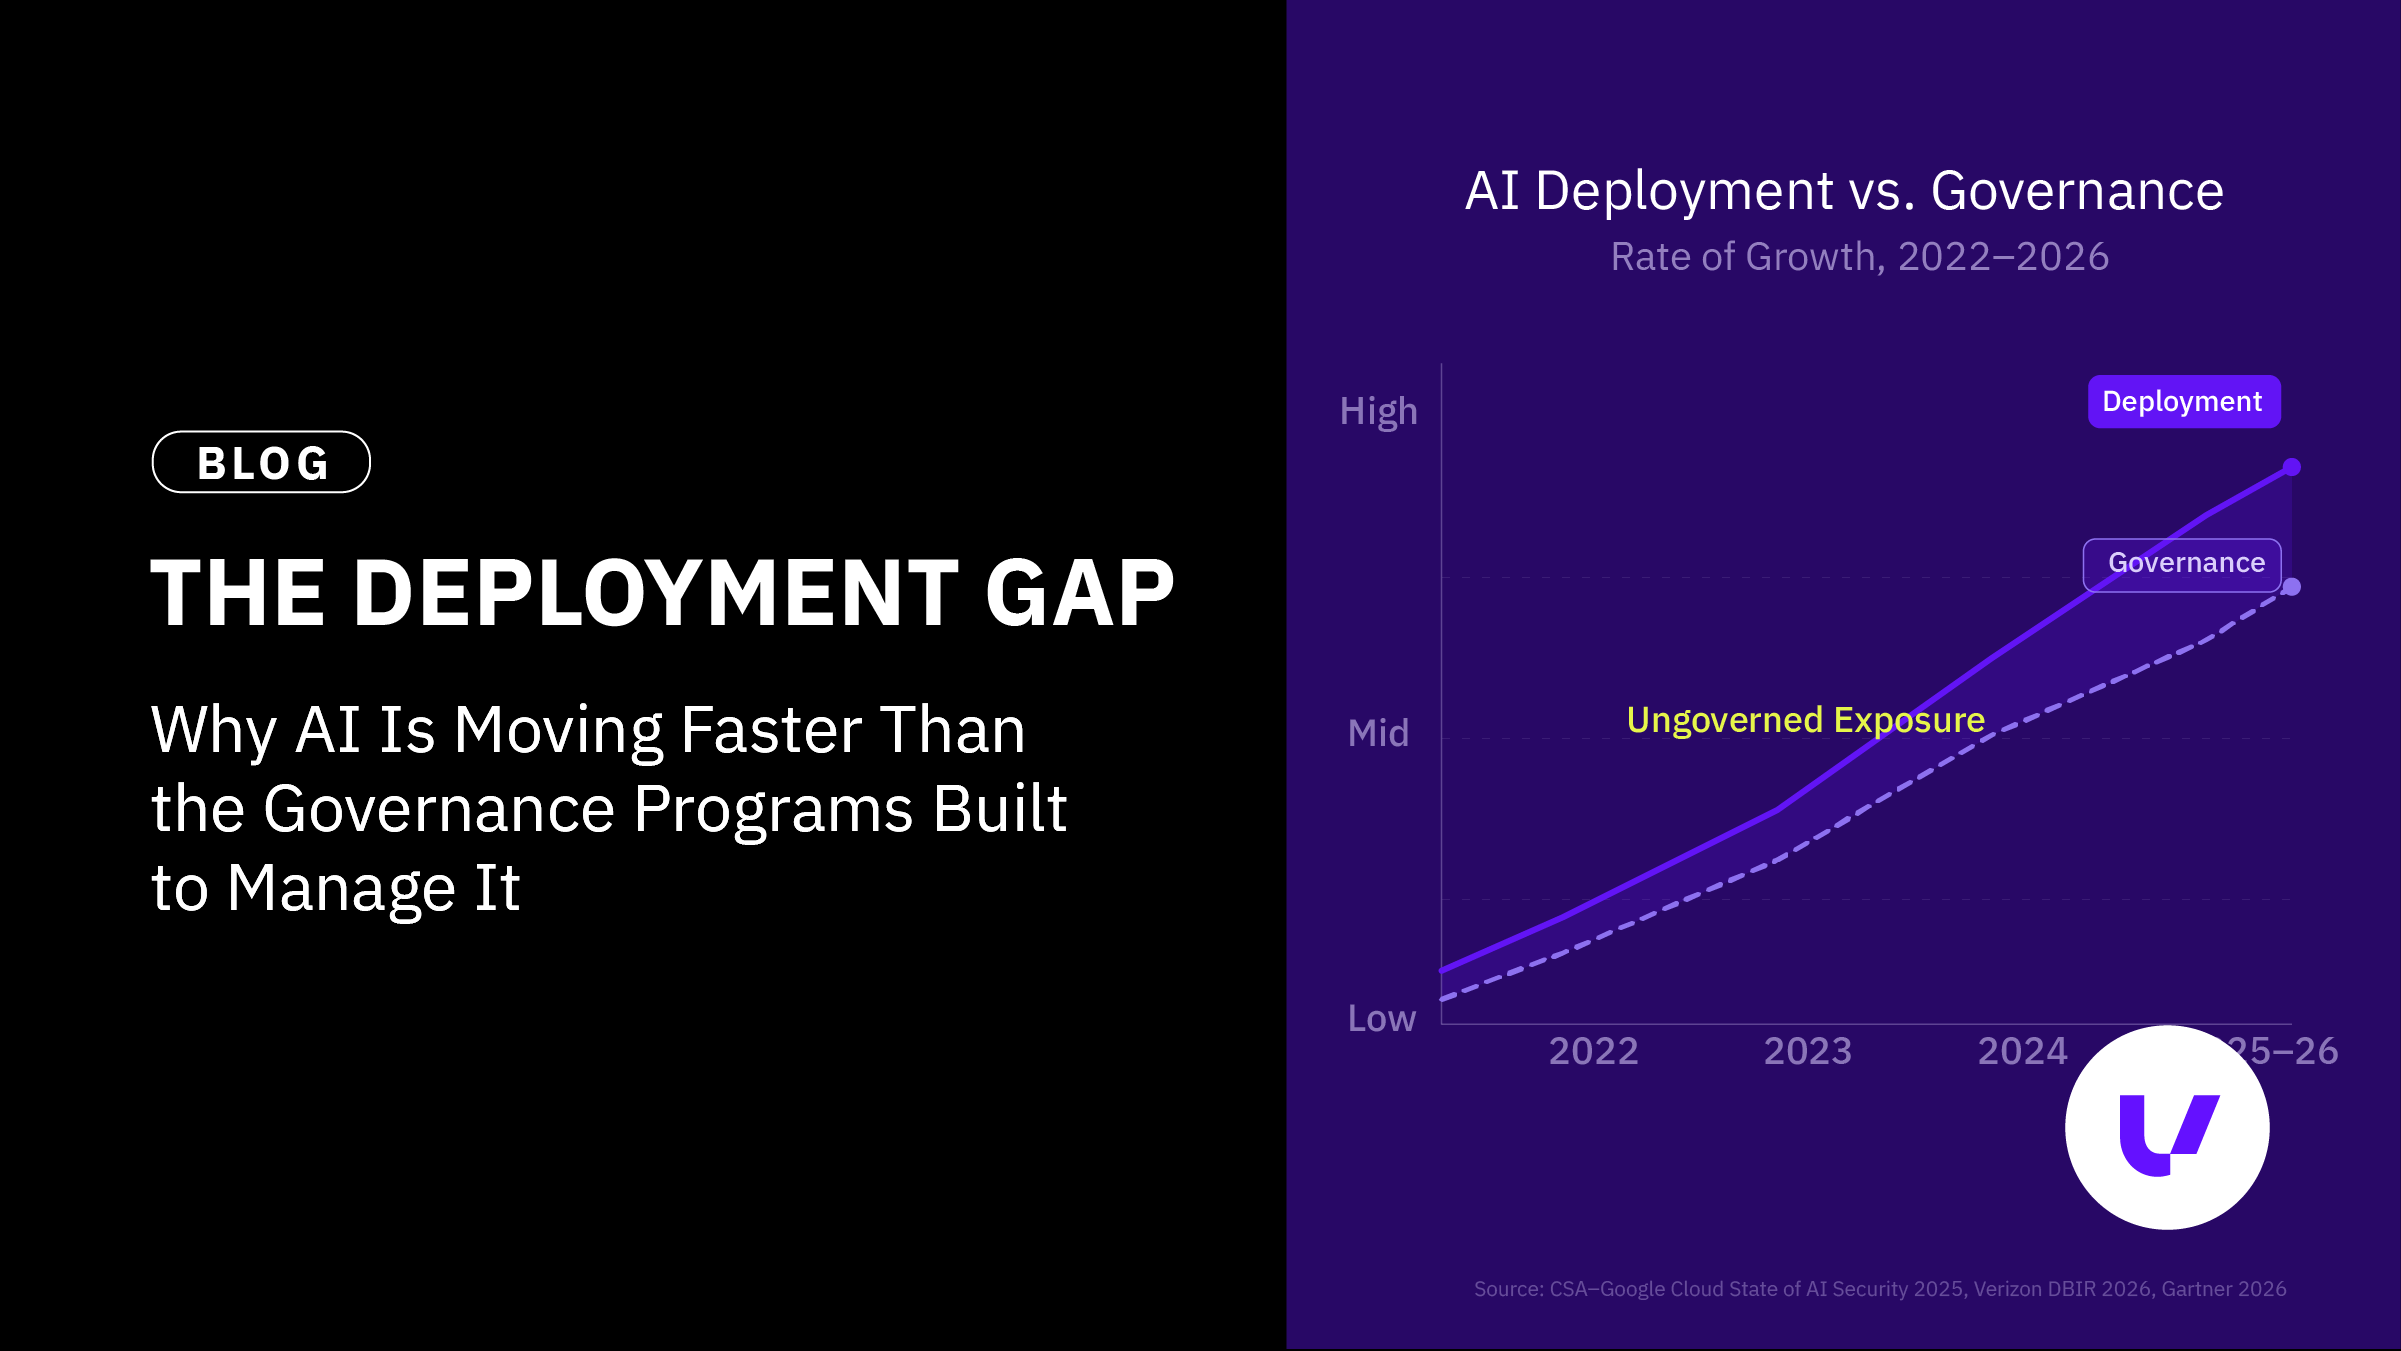
The NIST AI Risk Management Framework: The Foundation to Build Your AI Governance Program Upon
Three-quarters of companies have an AI policy. Few have a governance program. Here's why the NIST AI RMF is the framework to build one on.
Benchmarks your AI security practices against peer data.
Find flaws in AI Systems
Find flaws in web, mobile, and IoT applications.
Live-fire exercises to sharpen detection and response.
Time-boxed security assessments across networks, apps, and infrastructure.
Simulated attacks to test detection and incident response.
Named security experts integrated seamlessly into your team.
Real-time detection and automated threat response.
24x7 monitoring and response by expert analysts.
Detection-focused SIEM migration without visibility gaps.
UltraViolet's proprietary AI platform powering all application penetration testing.
Unified security platform powering all UV services.
Automated detection engineering across your security platforms.
Cross-platform toolkit for advanced red team ops.
UltraViolet Cyber provides security services across the AI lifecycle, combining strategy, threat modeling, adversarial testing, monitoring, and training to support secure AI adoption.
A global audit firm needed proof its AI assistant could withstand attack. UltraViolet tested it and its ...
Secure your code, infrastructure, and deployment pipelines before attackers exploit them.
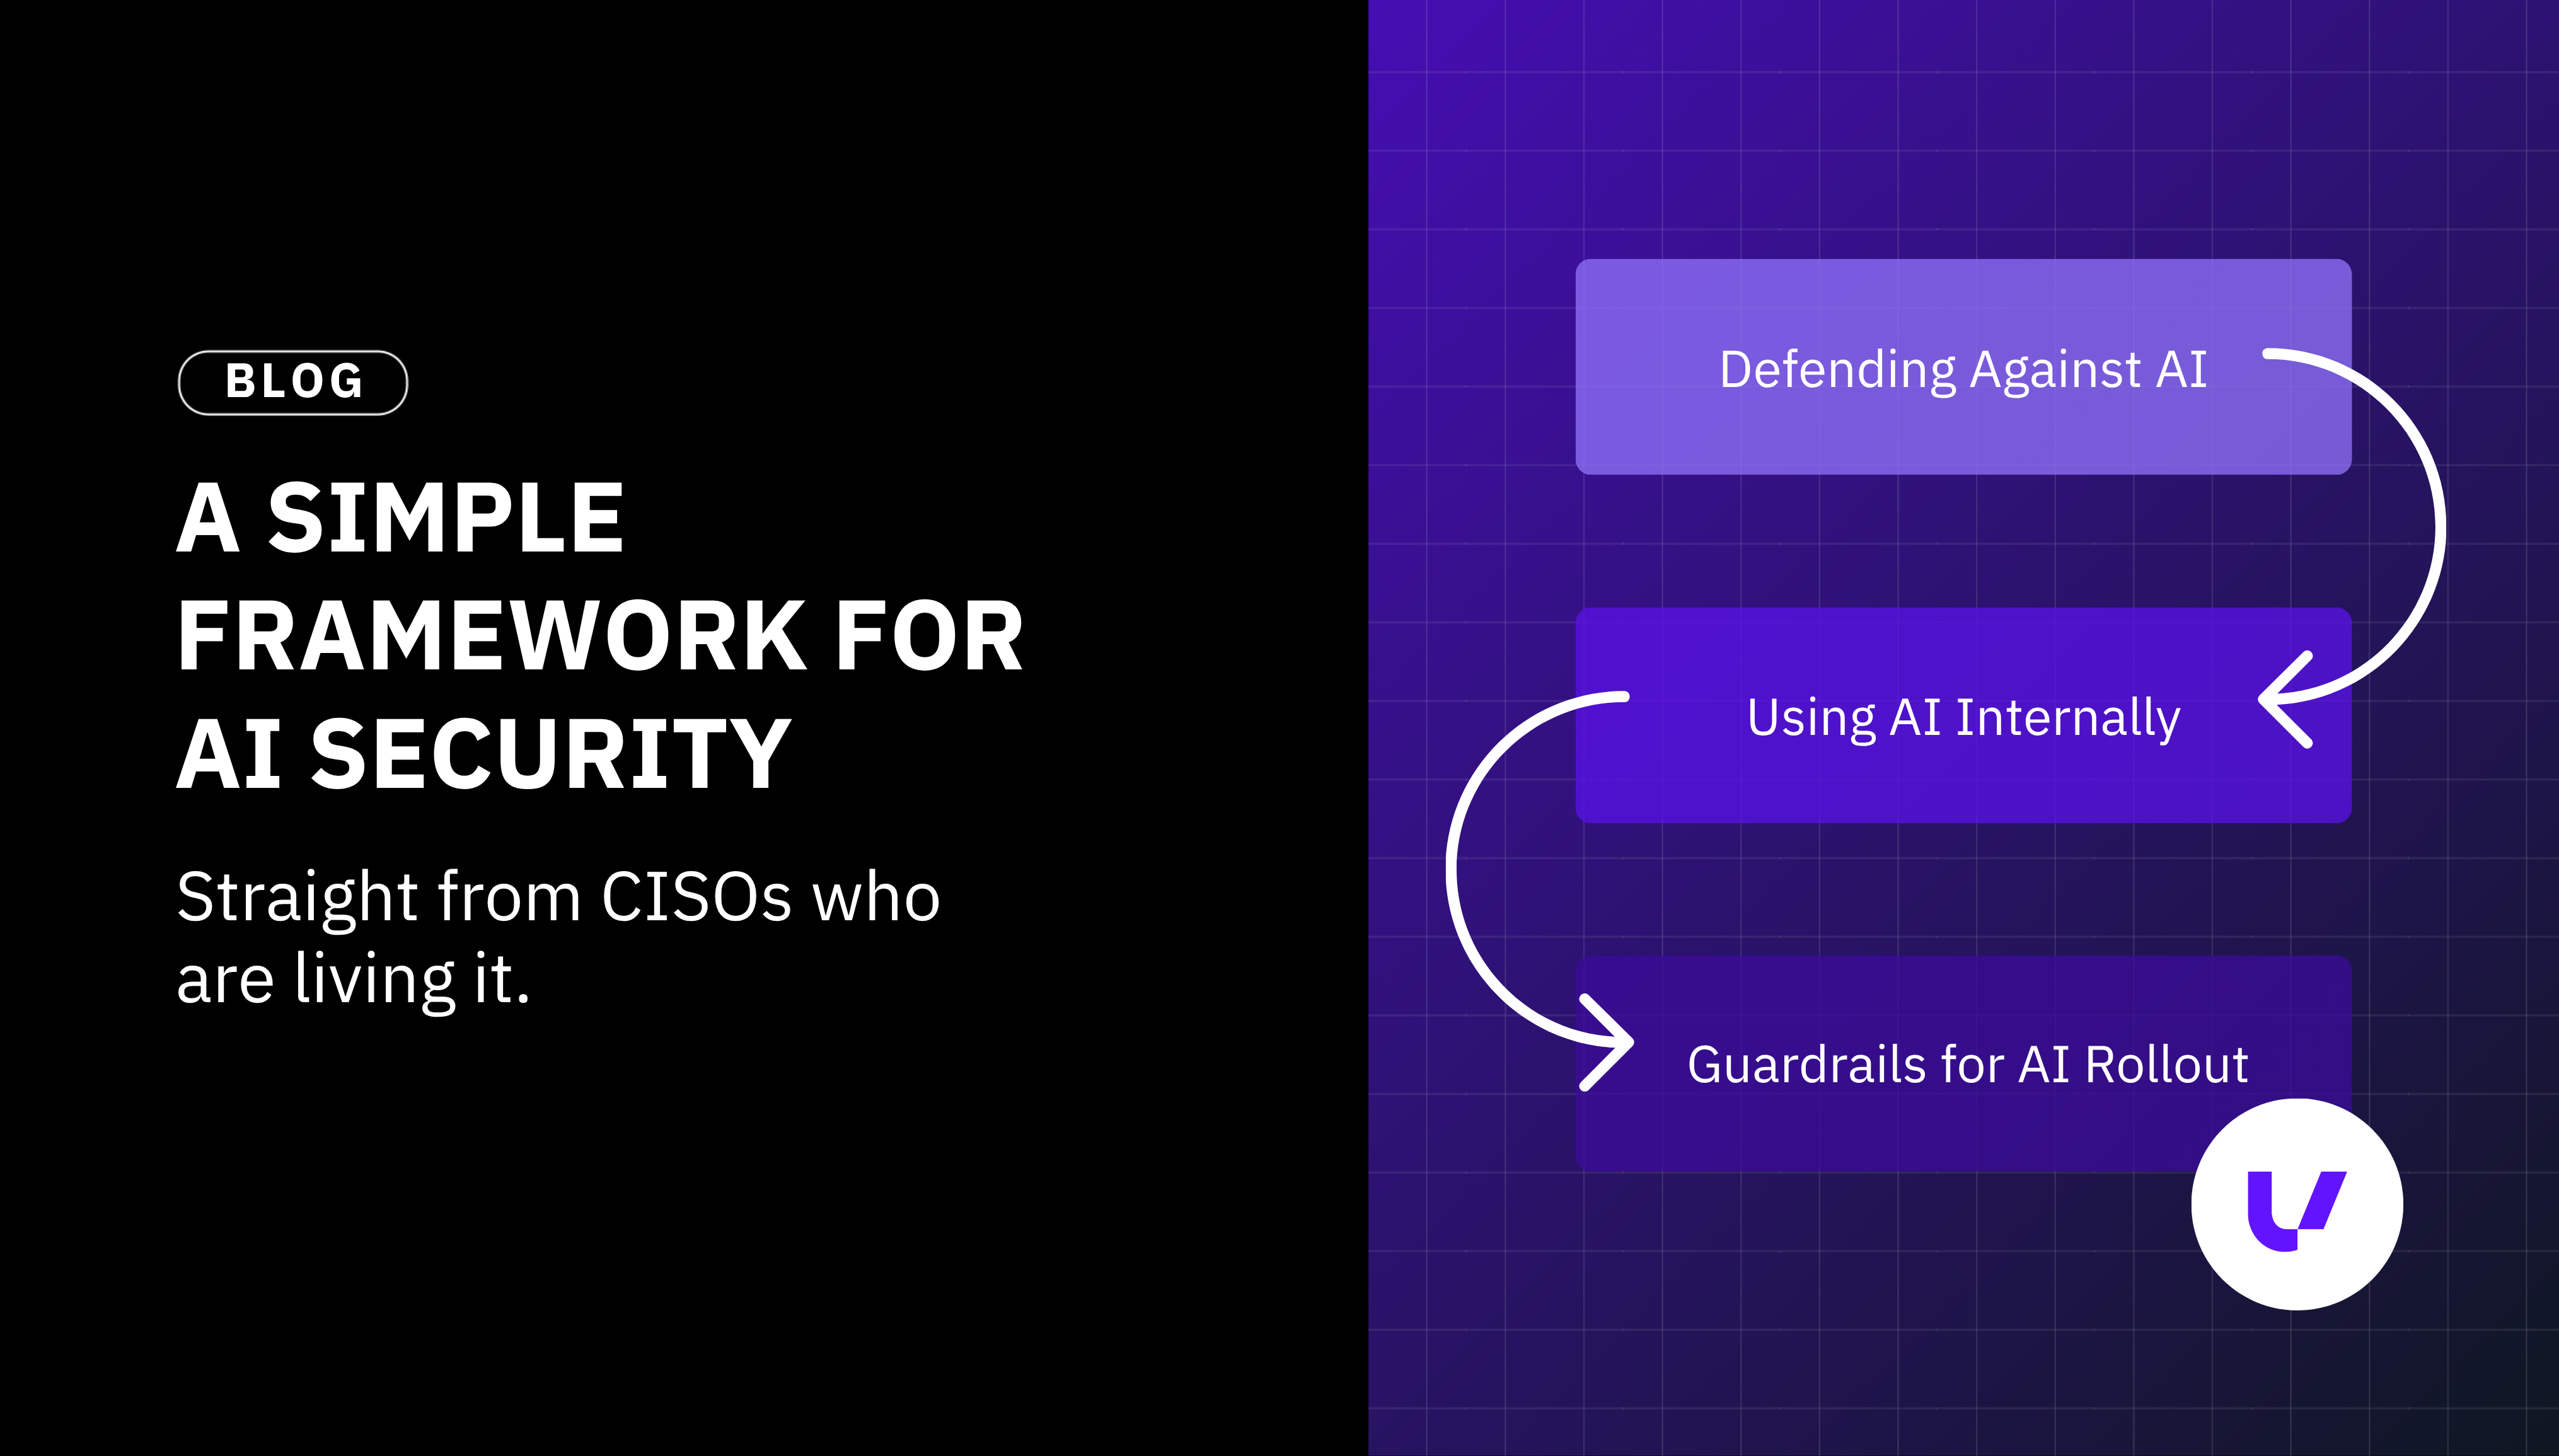
A three-part framework CISOs use to think about AI risk, backed by data on where most security programs are strong, and ...
UltraViolet's AISec Study uses an interview-based methodology to score AI security maturity across 10 organizations. Read ...
UltraViolet Cyber is a practitioner-led MSSP delivering offensive and defensive security to Global 2000 and Federal clients. Built by former intelligence operators, we unify application security, red teaming, detection, and engineering under one roof. Our UV Lens platform replaces silos with integrated, outcome-driven operations.
Confidential, interview-based assessment gives security leaders an evidence-based view of how organizations are actually governing, building and defending AI - replacing guesswork with data.
MCLEAN, Va. — August 27, 2026 — Today, UltraViolet Cyber (UltraViolet), the only security operations partner that unifies red, blue and purple team capabilities into one integrated offering, released findings from its AISec Study, an inaugural, interview-based benchmark of how organizations are actually securing and governing enterprise AI. Each engagement delivers a private report, benchmarking the organization against industry patterns and peer practices, together with prioritized recommendations for closing the gaps that matter most.
Most AI security guidance today is prescriptive, drawing on standards and checklists that describe what a program should look like. The AISec Study is different: It draws on a methodology similar to BSIMM (the Building Security In Maturity Model), a long-established benchmark for software security programs. The company designed the AISec Study to measure what organizations actually do, not what a framework says they should do. The study highlights findings from the banking and financial services, enterprise software, healthcare, manufacturing, hospitality, government and nonprofit sectors.
"This study gives security leaders something the industry hasn't had: a clear, evidence-based picture of where AI security programs actually stand, not where a checklist says they should be,” said Aravind Venkataraman, VP of Technology and AI Security, UltraViolet Cyber. “The pattern is consistent across every organization we assessed: the decisions have been made, and now the work is building the engineering and assurance to back them up. That's exactly where we help close the gap between tested and detected."
UltraViolet found that Governance & Policy was the strongest capability, while AI Incident Response was the weakest, and Direction & Oversight, Assurance & Protection and Engineering & Usage averaged in the middle — a consistent split between deciding what to do with AI and building the controls that defend it.
The gap shows up again when breadth is measured against depth. On average, participating organizations have started roughly 86% of the framework's activities but are depth-weighted at about 59% — a large difference between beginning a control and making it repeatable and enforced. Starting a control is the easy part; standardizing it is where coverage scores are won or lost.
The study's sharpest finding centers on how software now gets built. Every organization in the study has approved a variety of AI coding assistants, which is the single most adopted control observed. But the controls that would make that AI-driven development lifecycle accountable are still emerging: no organization has established a repeatable way to track which code an AI agent wrote, screen that code for license and IP risk or detect automated attacks targeting AI systems. Only one organization in this study has established detection for automated, AI-driven attack behavior.
Participants also aligned on the same open problem: giving non-human AI agents their own identities, scoping what they're allowed to do and containing the blast radius when something goes wrong. That capability was observed in some form at 80% of organizations, but was fully established at zero.
"The AISec Study gave us visibility into more data-driven insights to measure and improve our AI initiatives,” said Sandy Blackwell, Global Senior Director, Software Security, 74 Software. “This allows us to compare our practices against those of other organizations, and helps identify potential gaps as well as gauge what to prioritize in terms of improvements. We are looking forward to continuing to work with the AISec benchmark team."
About the AISec Study
The AISec Study is practitioner-led. Each participating organization is assessed through confidential interviews with security, AI, governance and engineering leadership, and every organization is measured against the same catalog so that results are comparable across the data pool. Figures reflect the ten organizations assessed to date and are shifting as the data pool grows with observations from the second cohort of organizations, which are already in progress.
Organizations that want the same view of their own AI security posture don’t have to wait for the next phase of the study. UltraViolet offers its AI Security Program Assessment as a standalone engagement, applying the same AISec methodology through confidential interviews with security, governance and product teams. To learn more or schedule the assessment, visit UltraViolet Cyber.
About UltraViolet Cyber
UltraViolet Cyber is the only security operations partner that unifies red, blue, and purple team capabilities into one integrated team — finding what's vulnerable, stopping active threats, and validating that your defenses hold under real pressure. Built by former U.S. intelligence community operators with 30+ years of experience, we serve 400+ Global 2000 enterprises and federal agencies. Our practitioner-led and AI-accelerated closed-loop operations turn offensive findings into defensive weapons immediately so gaps close in real time and defenses improve before attackers can exploit what testing uncovers. Offense informs defense. Defense sharpens offense. Security that gets smarter and stronger with every iteration.
UltraViolet is at the forefront of AI security. Purpose-built to test, validate, and govern the AI systems organizations are deploying today, UltraViolet brings the same offensive and defensive rigor to AI that it applies across the enterprise. UltraViolet is ranked #19 on the Top 250 MSSP List and is headquartered in McLean, Virginia. For more information, visit our website, read our blog, or follow us on LinkedIn.
Media Contact
W2 Communications for UltraViolet Cyber ultraviolet@w2comm.com
We’re here to help. Get in touch for an initial conversation with one of our security experts and learn more about how UltraViolet Cyber can help you take cyber readiness and resilience to new levels.