Scaling Security Testing Without Starting Over
How a Fortune 100 technology company extends its offensive security team with UltraViolet Cyber, testing web, mobile, client, and embedded systems entirely within the customer’s environment.
Benchmarks your AI security practices against peer data.
Find flaws in AI Systems
Find flaws in web, mobile, and IoT applications.
Live-fire exercises to sharpen detection and response.
Time-boxed security assessments across networks, apps, and infrastructure.
Simulated attacks to test detection and incident response.
Named security experts integrated seamlessly into your team.
Real-time detection and automated threat response.
24x7 monitoring and response by expert analysts.
Detection-focused SIEM migration without visibility gaps.
UltraViolet's proprietary AI platform powering all application penetration testing.
Unified security platform powering all UV services.
Automated detection engineering across your security platforms.
Cross-platform toolkit for advanced red team ops.
UltraViolet Cyber provides security services across the AI lifecycle, combining strategy, threat modeling, adversarial testing, monitoring, and training to support secure AI adoption.
A global audit firm needed proof its AI assistant could withstand attack. UltraViolet tested it and its ...
Secure your code, infrastructure, and deployment pipelines before attackers exploit them.
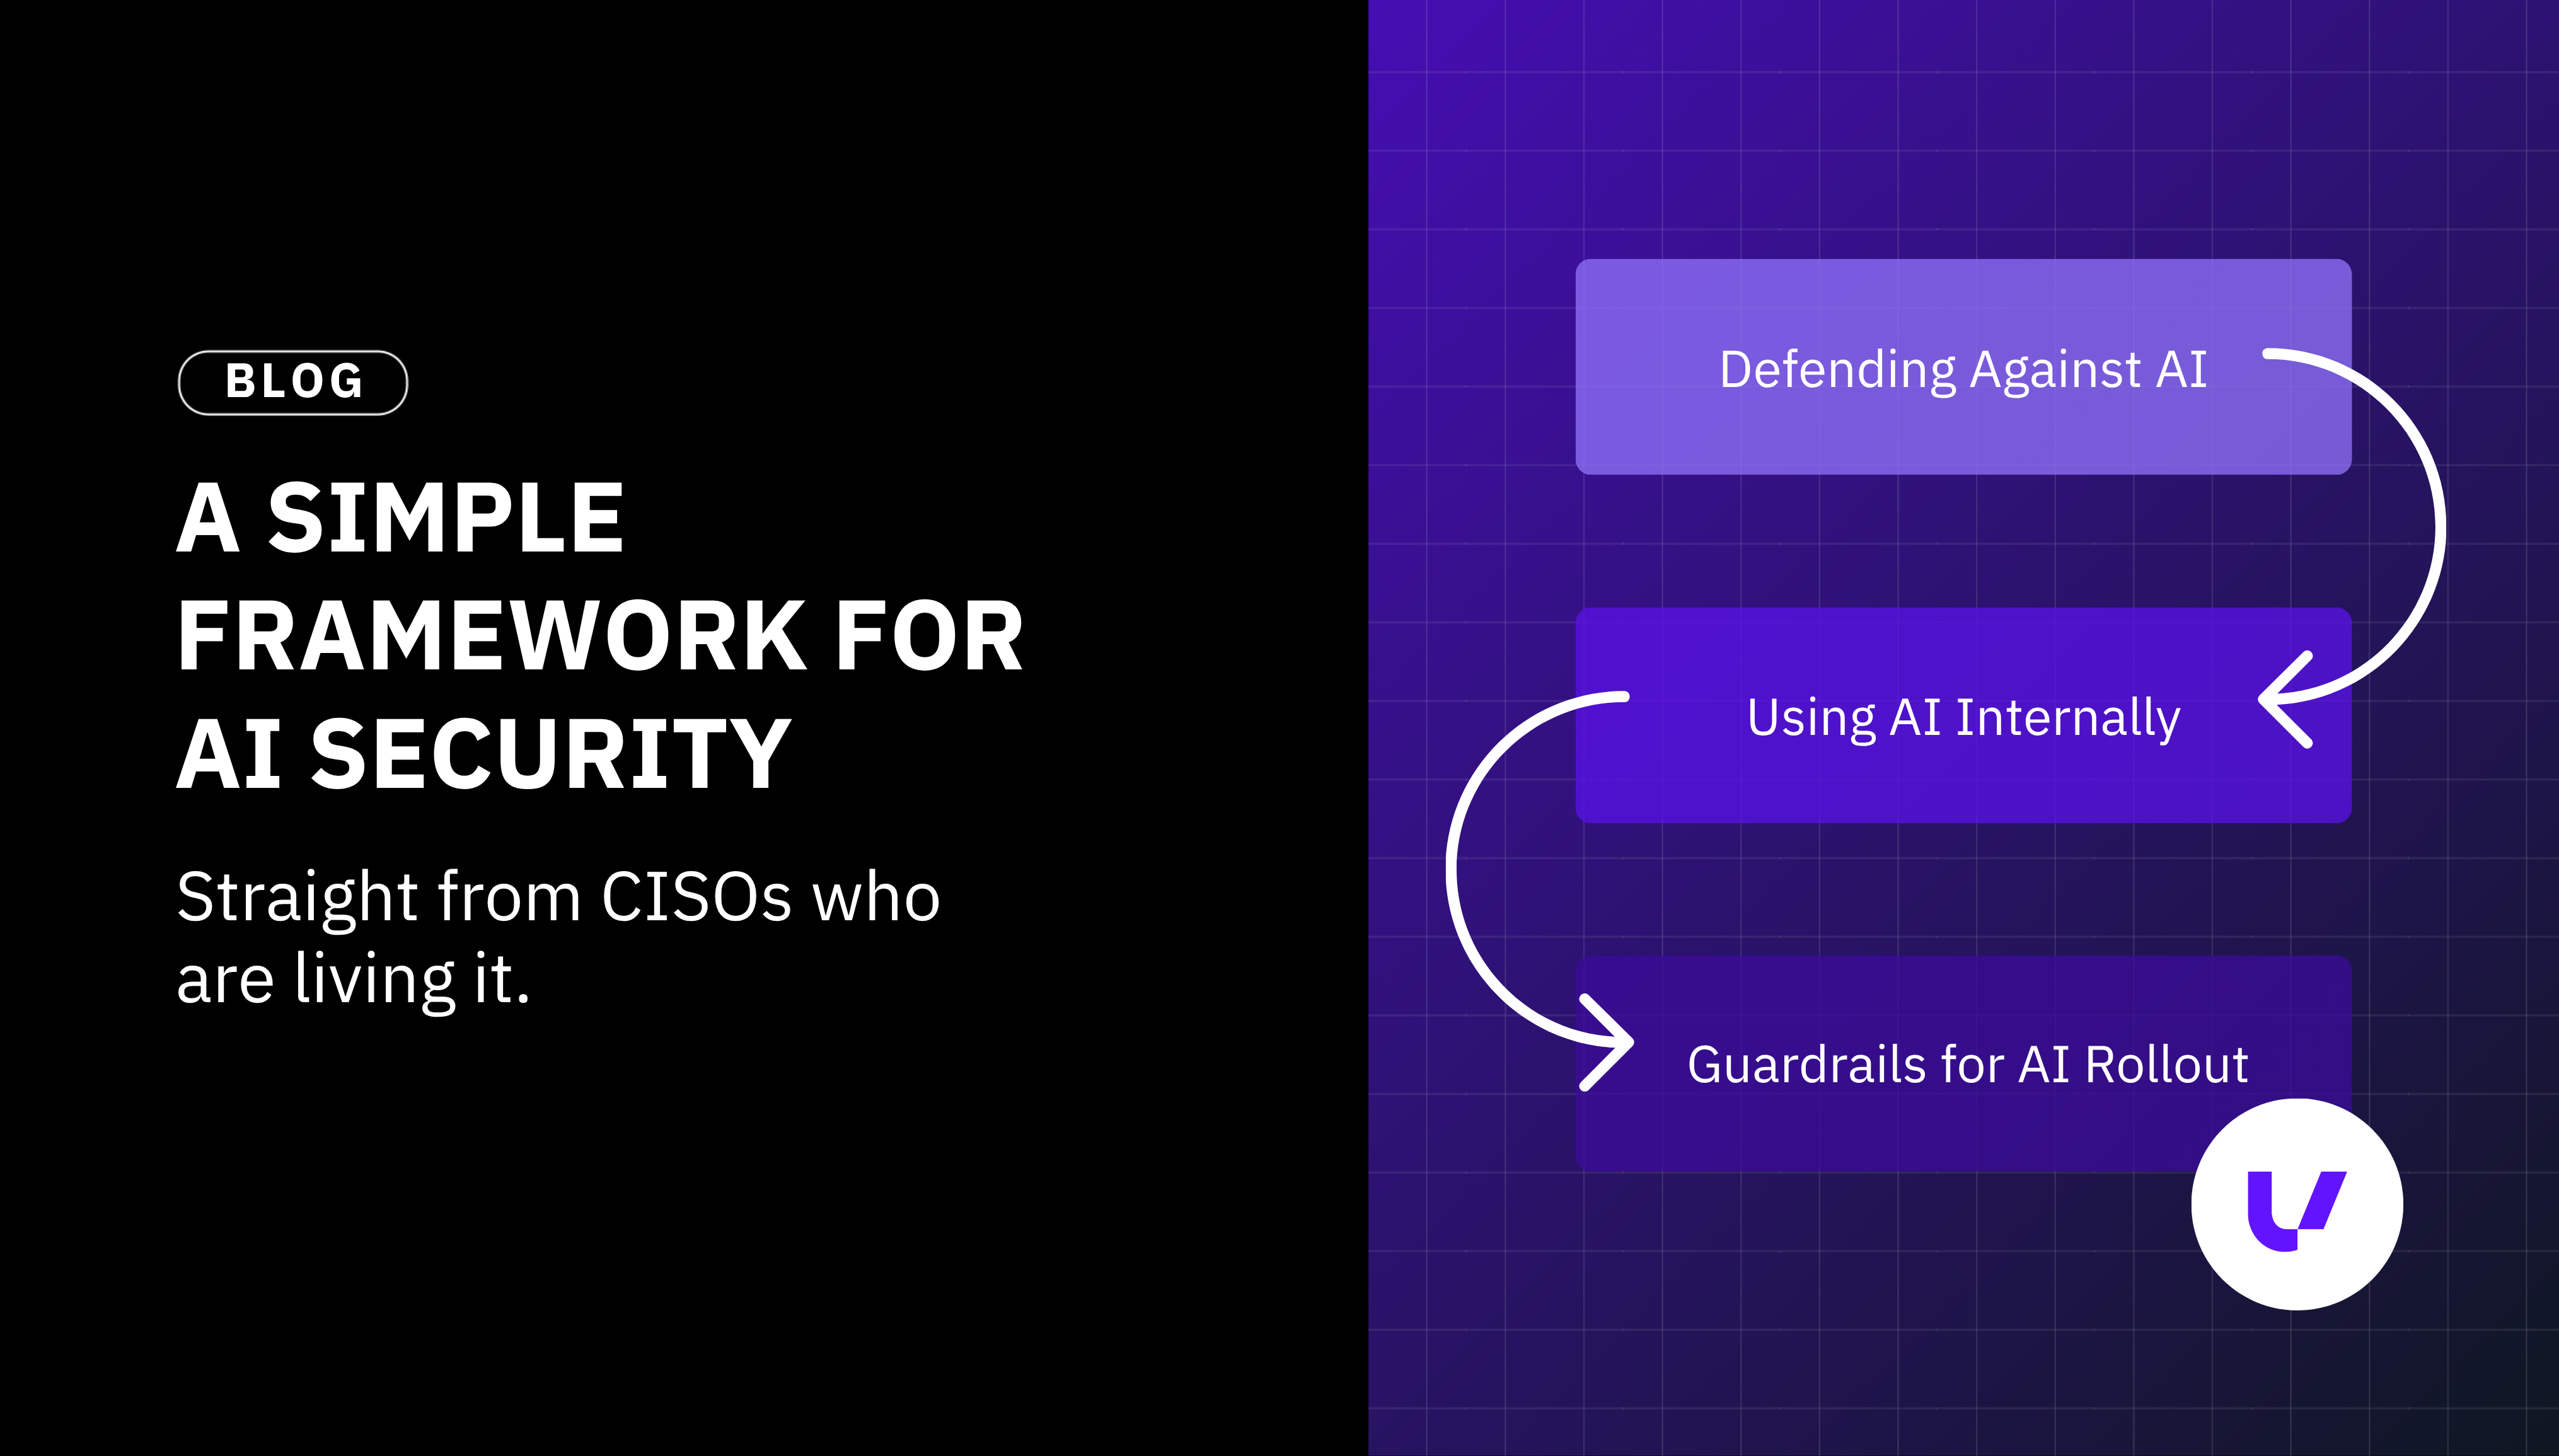
A three-part framework CISOs use to think about AI risk, backed by data on where most security programs are strong, and ...
UltraViolet's AISec Study uses an interview-based methodology to score AI security maturity across 10 organizations. Read ...
UltraViolet Cyber is a practitioner-led MSSP delivering offensive and defensive security to Global 2000 and Federal clients. Built by former intelligence operators, we unify application security, red teaming, detection, and engineering under one roof. Our UV Lens platform replaces silos with integrated, outcome-driven operations.
How a global financial software company keeps hundreds of marketplace applications moving through a repeatable security gate each year.
10+ Years of Partnership
Supporting the customer's third-party security program
~60 Priority Tests Active at Any Time
Continuous testing cadence across hundreds of developers
9+ Dedicated Assessors
Steady team supporting an ongoing assessment queue
A global financial software company offers hundreds of third-party applications and integrations through its marketplace. These are built by small development teams and established software companies alike.
Each application carries different risks. Some handle basic data processing, while others work with sensitive information, including financial records and Social Security numbers. A vulnerability in any one of them can expose customer data and damage trust in the company.
Every application must pass a penetration test before entering the marketplace and be retested annually to remain listed. Premium listings generate revenue for the company, but the testing requirements apply to every tier.
When the company first turned to UltraViolet, its internal security team was already stretched thin. Its red team was focused on black-box testing of live production systems, leaving a gap in the pre-production testing needed to approve marketplace listings.
As the marketplace grows, the company has to coordinate hundreds of assessments with developers whose security experience varies widely. For many, this is their application's first penetration test. Some developer teams have only a handful of engineers, and routine compliance steps such as signing a testing affidavit can prompt their leadership to ask what they're agreeing to. Each assessment involves defining the testing scope, collecting compliance documentation, and explaining findings so developers can act on them.
The company needs testing capacity that meets specific staffing and reporting requirements. Anyone who accesses U.S. tax data must be based in the United States, which rules out offshore delivery for those engagements.
Every assessor must also hold recognized security certifications. For money-movement applications that process high dollar volumes, the company reviews assessors’ resumes and interviews them before approving their participation.
The company also needs formal, well-documented external testing reports that meet its standards for rigor and support internal reviews.
UltraViolet has met these requirements year after year. As the company pursues ISO/IEC 27001 certification, UltraViolet's testing also provides evidence to support that certification work.
Keeping this testing external was a deliberate build-versus-buy decision. Contracted capacity was easier to secure than new full-time headcount, and external testing also supports the company’s certification work.
Today, UltraViolet fills that pre-production testing gap as the company’s Virtual Security Team (VST), providing ongoing application security support as an extension of its product security team.
A dedicated program manager coordinates the work of nine dedicated assessors, managing assessments from intake through completion and overseeing developer coordination.
With roughly 60 assessments active at any time, new assessments begin as others conclude, sustaining a steady testing cadence throughout the year.
The company previously handled developer coordination in-house, but found that it took time away from the security team's other work. UltraViolet now handles most of that coordination, from onboarding and collecting SOC 2 documentation and other artifacts to explaining findings and helping developers complete the steps needed to move forward. This guidance is especially valuable for teams new to security testing.
Every assessment starts with a review of the application: how critical it is, what data it handles, how technically complex it is, and what has changed since any previous assessment. UltraViolet and the company use these factors to define the testing scope.
Applications that handle sensitive data, such as Social Security numbers, receive a full, in-depth assessment, while lower-risk applications receive a narrower, focused assessment.
Several applications in the marketplace are mobile. For these applications, UltraViolet provides hands-on, manual testing to complement the program’s largely automated assessment coverage.
"You do a great job of finding vulnerabilities in mobile applications specifically," the security operations manager said. "This is one of the only places where we're doing manual testing, and the reporting we get back is very helpful."
Stronger remediation and developer requirements
With UltraViolet’s input, the company updated its program to require remediation and retesting of critical and high-severity findings. A developer’s confirmation alone is no longer enough. Applications with critical findings cannot enter the marketplace until those findings are resolved or a formal exception is granted.
UltraViolet's assessors also flagged a gap between what their reports covered and the security requirements the company published for developers. The company used that feedback to update its guidance.
Evidence for leadership and audit reviews
Assessment findings feed weekly risk reporting to leadership. The company tracks remediation SLAs by severity, ranging from seven days for critical third-party findings to 90 days for low-severity findings. The team reports adherence each week to a CISO who reports directly to the CEO. UltraViolet’s structured reports support that tracking and provide evidence for audit reviews.
The company's data analysts also pull assessment findings into operational dashboards through UltraViolet's APIs, helping leadership track risk across the marketplace and make informed decisions. With some other testing vendors, the company receives static PDF reports and must manually re-enter findings as tickets before engineers can act on them.
Consistent capacity through organizational change
The relationship spans 10+ years and has grown from individual assessments to quarterly engagements and now to an annual program. The ongoing program gives the company a repeatable way to manage third-party application risk as its marketplace grows.
The program has maintained its testing capacity through reorganizations, changes in program ownership, and acquisition transitions on the partner side. Established relationships and trust help the teams preserve continuity through these changes.
Weekly meetings give the company regular access to the UltraViolet team to discuss questions, priorities, and improvements.
"I don't meet with any other vendor on a weekly basis," the security operations manager said. "I get a lot of information every week, and we're all interested in learning and growing together."
For the company’s security operations manager, a former NSA red teamer, finding a vulnerability is the beginning of a much longer process. He values UltraViolet’s support in helping the team work through findings and act on them.
"Identifying the hole is step one in a fifty-step process," the security operations manager said. "Partnership is the most important thing from a business perspective."
Alongside its remediation and retesting requirements, the company is working toward a more current picture of application risk between annual assessments. Both teams see this as an opportunity to strengthen the program.
As third-party developers build more AI-driven features into their applications, they are beginning to request assessments of those components. Both teams are also discussing how the relationship could grow beyond penetration testing into broader offensive and defensive security work.
UltraViolet’s understanding of the company’s requirements and its established relationships with developers provide a foundation for this next phase, helping the teams address new assessment needs while keeping ongoing testing moving.
Give your team support from dedicated practitioners who manage ongoing testing and developer coordination, helping you keep pace as your application portfolio grows.
Let’s talk about your testing needs and how UltraViolet could support your team.
We’re here to help. Get in touch for an initial conversation with one of our security experts and learn more about how UltraViolet Cyber can help you take cyber readiness and resilience to new levels.