Meet Andrew Park, UltraViolet Cyber's New Chief Information Security Officer
We're glad to introduce Andrew Park as UltraViolet Cyber's new Chief Information Security Officer.
Benchmarks your AI security practices against peer data.
Find flaws in AI Systems
Find flaws in web, mobile, and IoT applications.
Live-fire exercises to sharpen detection and response.
Time-boxed security assessments across networks, apps, and infrastructure.
Simulated attacks to test detection and incident response.
Named security experts integrated seamlessly into your team.
Real-time detection and automated threat response.
24x7 monitoring and response by expert analysts.
Detection-focused SIEM migration without visibility gaps.
UltraViolet's proprietary AI platform powering all application penetration testing.
Unified security platform powering all UV services.
Automated detection engineering across your security platforms.
Cross-platform toolkit for advanced red team ops.
UltraViolet Cyber provides security services across the AI lifecycle, combining strategy, threat modeling, adversarial testing, monitoring, and training to support secure AI adoption.
How a Fortune 100 technology company extends its offensive security team with UltraViolet Cyber, testing web, ...
Secure your code, infrastructure, and deployment pipelines before attackers exploit them.
Before you trust a MITRE ATT&CK coverage number, run it through three questions. Here's what to ask, and why each one ...
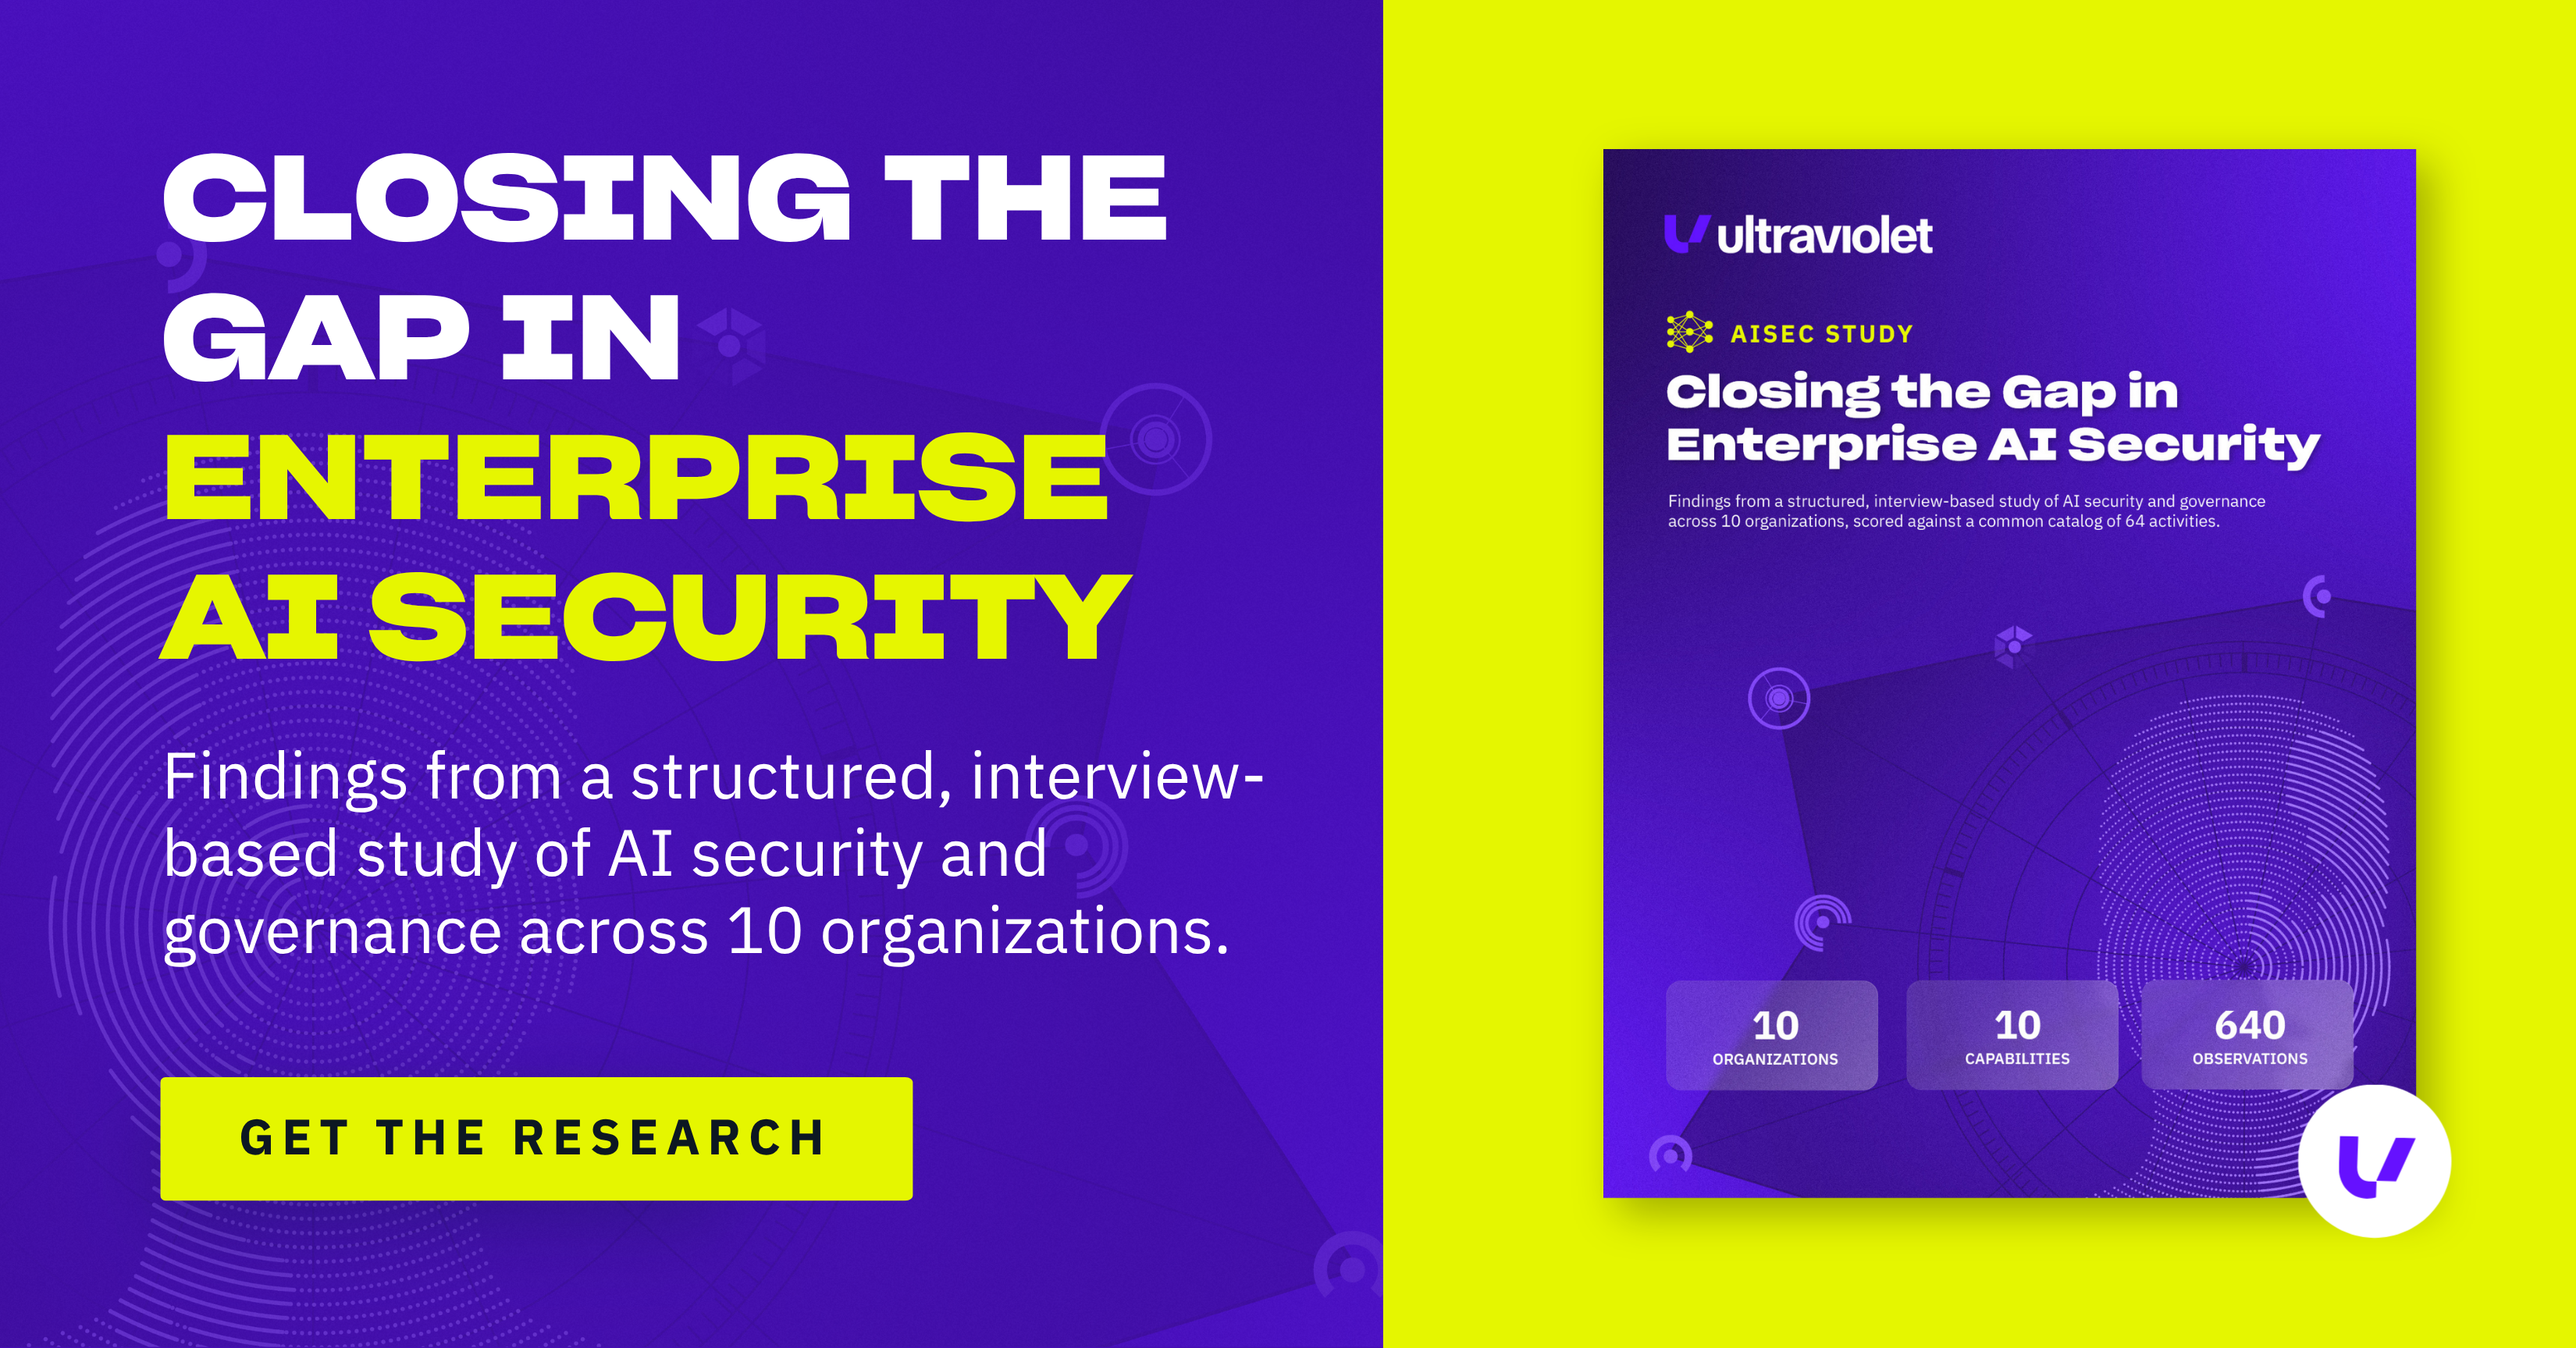
UltraViolet's AISec Study uses an interview-based methodology to score AI security maturity across 10 organizations. Read ...
UltraViolet Cyber is a practitioner-led MSSP delivering offensive and defensive security to Global 2000 and Federal clients. Built by former intelligence operators, we unify application security, red teaming, detection, and engineering under one roof. Our UV Lens platform replaces silos with integrated, outcome-driven operations.
UltraViolet Cyber
MuddyWater, the Iranian cyber espionage group associated with Iran’s Ministry of Intelligence (MOIS) has leaked part of their new backdoor tool, dubbed ‘BugSleep’. This advanced persistent group (APT) is known for exploiting compromised enterprise environments to send phishing emails to compromise other environments. The group has been more active after the October 2023 conflict between Israel and Hamas. While MuddyWater is still developing this new backdoor tool, researchers have already documented command and control tactics within the currently available sample.
MuddyWater, also known as ‘Earth Vetala’, ‘MERCURY’, and ‘Static Kitten’, is believed to have started operations as far back as 2017. The group primarily targets Israel, with other notable activity within the Middle East, Asia, North America, Europe and Africa. Much of their work focuses on cyberespionage, with their targets aligning with government and private organizations of interest to the state of Iran.
Check Point researchers recently shared a change in attack pattern associated with MuddyWater (MW). Previously, MW would send a spear phishing email to targets within a specific industry to prompt the recipient to download the Atera remote management tool from an Egnyte-hosted page. MW now added a variation where the spear phishing email contains a PDF with an embedded link to download the BugSleep backdoor.
Once downloaded, the backdoor sleeps for a period. This is a common tactic to avoid detection within researcher sandboxes. The payload then extracts the encrypted configuration file and calls out every 30 minutes to the command and control (C2) server for further instructions. The communications to the C2 server are also encrypted, further increasing the difficulty of detection from security tools.
A variant of the custom loader injected encrypted shellcode into the running memory of Edge, Chrome, Opera, AnyDesk, OneDrive and Powershell to further avoid detection. MuddyWater has used Telegram APIs to establish encrypted C2 communications in the past, with their ‘Small Sieve’ Python backdoor back in late 2021. Other encrypted channels may be added to BugSleep in future iterations.
Gatlan, S. (2024, July 15). New BugSleep malware implant deployed in MuddyWater attacks. BleepingComputer. Retrieved from https://www.bleepingcomputer.com/news/security/
(2024, July 15). New BugSleep Backdoor Deployed in Recent MuddyWater Campaigns. Check Point Research. Retrieved from https://research.checkpoint.com/2024/new-bugsleep-backdoor-deployed-in-recent-muddywater-campaigns/
(2024, July 15) MuddyWater. MITRE | ATT&CK. Retrieved from https://attack.mitre.org/groups/G0069/
(2022, January 27). Small Sieve. National Cyber Security Centre. Retrieved from https://www.ncsc.gov.uk/files/NCSC-Malware-Analysis-Report-Small-Sieve.pdf
(2024, July 15). Manage approved apps for Windows devices with App Control for Business policy and Managed Installers for Microsoft Intune. Microsoft Learn. Retrieved from https://learn.microsoft.com/en-us/mem/intune/protect/endpoint-security-app-control-policyWe’re here to help. Get in touch for an initial conversation with one of our security experts and learn more about how UltraViolet Cyber can help you take cyber readiness and resilience to new levels.